Feature #4221
closed

Force passwords to contain specified character classes
Description
I would like to enforce strong password for users in redmine. As if now redmine will accept any four letter password. Is there a way that applicaton checks how strong a password is when a new user register in it.
Can we implement any password generator with redmine?
Files
 Updated by Jean-Philippe Lang about 17 years ago
As of r2678, you can specify the minimum password length in settings.
But a minimum password strength setting could be also added (eg. Fair, Strong, Very strong) using kind of password strengh meter.
Updated by Jean-Philippe Lang almost 17 years ago
- Category set to Accounts / authentication
 Updated by Henrik Ammer almost 17 years ago
Jean-Philippe Lang wrote:
But a minimum password strength setting could be also added (eg. Fair, Strong, Very strong) using kind of password strengh meter.
I would love to see this!
 Updated by Samuel Suther over 13 years ago
*1
 Updated by @ go2null over 13 years ago
 Updated by Toshi MARUYAMA over 13 years ago
- Related to Feature #3872: New user password - better functionality added
 Updated by Simon O over 12 years ago
1
The new feature implemented in 2.4.0+ referring to Feature #3872 includes a secured password generator.
However, if users may change their password at first login, they may pick "aaaaaaaa" which is far away from being secure. Thus, I also recommend to add a kind of password security check as suggested by jim joseph.
Please reopen ticket.
Thanks a lot!
 Updated by Aleksandar Pavic almost 11 years ago
+1
There are some recent efforts as I can see.
https://github.com/simonswine/redmine_password_tool
https://github.com/go2null/redmine_account_policy
But this should be a core system feature, it is a must for enterprise use.
Updated by Toshi MARUYAMA almost 10 years ago
- Has duplicate Feature #25054: Enforcing Strong Password in Redmine added
 Updated by Go MAEDA over 7 years ago
- Related to Feature #3155: Password policy and secure logon procedure added
 Updated by Takenori TAKAKI over 7 years ago
If we can enforce password strength, Redmine will be used in environments where some security policy is required.
I post a patch, as I implemented the following features:
- Enable to setting password strength in admin settings
- Enable to selecting the enforce character types (Uppercase, Lowercase, Digits, Special characters).
- Validation for each enforce character types
Updated by Go MAEDA over 7 years ago
- Priority changed from High to Normal
- Target version set to Candidate for next major release
Updated by Go MAEDA over 7 years ago
I think the validation in enforce-password-char-types.patch should cover all ASCII special characters, such as '(', ')', '+', '-', and '_'. The following code does that.
diff --git a/app/models/setting.rb b/app/models/setting.rb
index b18f8ed89..4171fa04e 100644
--- a/app/models/setting.rb
+++ b/app/models/setting.rb
@@ -19,6 +19,13 @@

 class Setting < ActiveRecord::Base

+  PASSWORD_REQUIRED_CHARACTER_CLASSES = {
+        'uppercase'          => /[A-Z]/,
+        'lowercase'          => /[a-z]/,
+        'digits'             => /[0-9]/,
+        'special_characters' => /[[:ascii:]&&[:graph:]&&[:^alnum:]]/
+    }
+
   DATE_FORMATS = [
         '%Y-%m-%d',
         '%d/%m/%Y',
Updated by Takenori TAKAKI about 7 years ago
I change a patch and post it again.
- Changed definition of 'special_characters' to the code proposed by Mr. Maeda
- Changed regular expression in validation of special characters. => Almost all special characters within the ASCII range can be used.
- Shortened constant and label names.
- On password generation, contain special characters only when special characters are required.
- Added display of usable characters such as "Change Password" Form.
Updated by Go MAEDA about 7 years ago
- Target version changed from Candidate for next major release to 4.1.0
LGTM. Setting the target version to 4.1.0.
Updated by Go MAEDA about 7 years ago
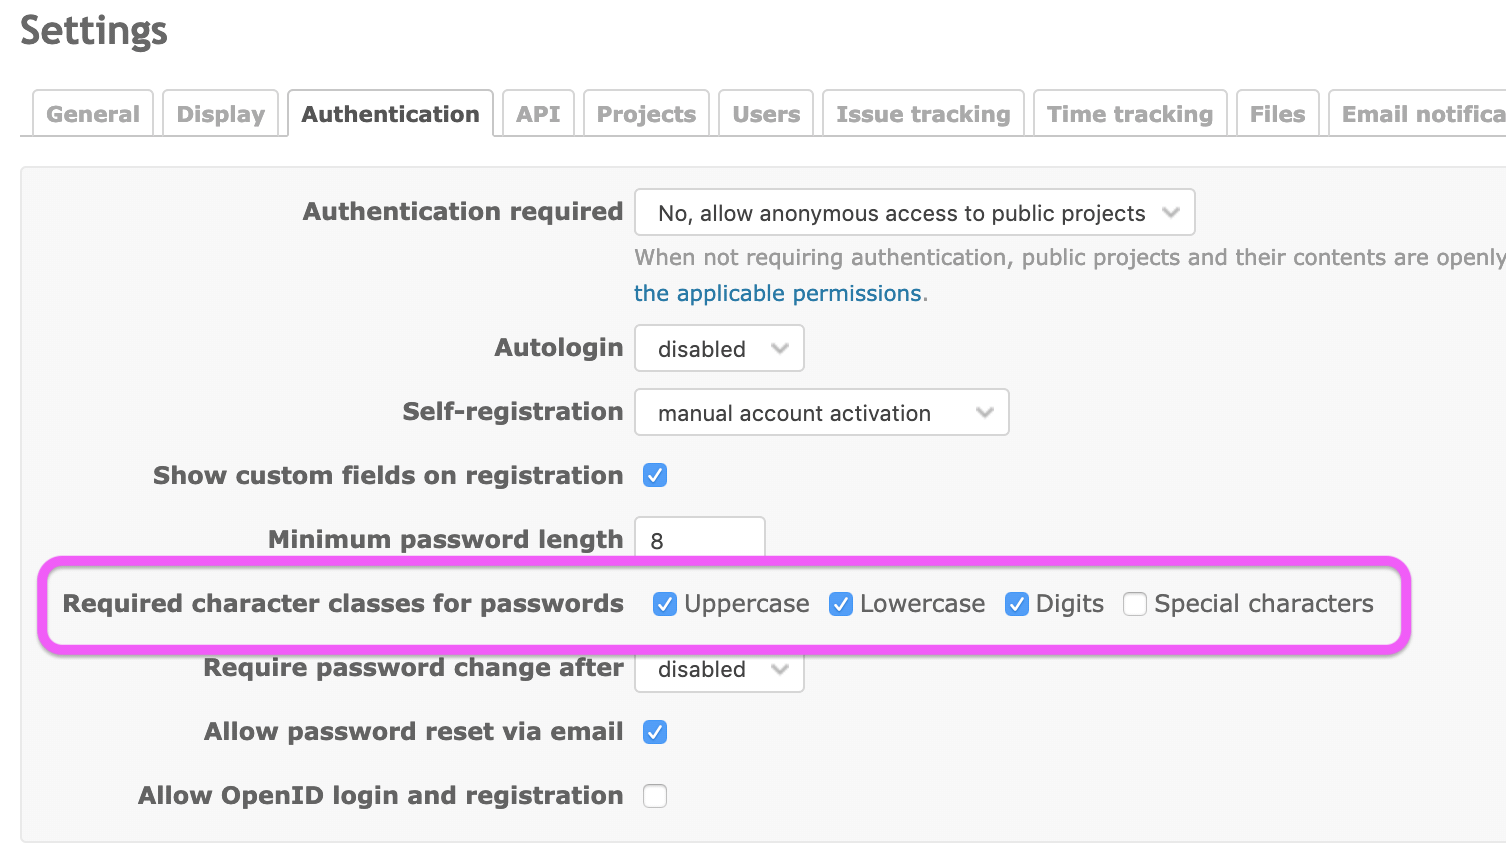
- File setting-required-character-classes-for-passwords@2x.png setting-required-character-classes-for-passwords@2x.png added
This is the screenshot of enforce-password-char-types-v2.patch. Admins can force users to include specified character classes (uppercase, lowercase, digits, or special Characters) in their password. This feature must be welcomed by many admins.
Updated by Go MAEDA about 7 years ago
- Subject changed from Enforcing Strong Password for Users to Force passwords to contain specified character classes
- Status changed from New to Closed
- Assignee set to Go MAEDA
- Resolution set to Fixed
Committed the patch. Thank you for improving Redmine.
Updated by Go MAEDA over 4 years ago
- Related to Defect #37449: Passing a wrong parameter to `with_settings` in UserTest::test_random_password_include_required_characters added